Cybersecurity Treaties 2026: U.S. Data Protection Guide for Citizens
Anúncios
Cybersecurity Treaties: A 2026 Guide for U.S. Citizens on Protecting Personal Data in an Interconnected World (Practical Solutions)
In an era defined by ubiquitous digital connectivity, the security of personal data has transcended national borders to become a global imperative. For U.S. citizens, navigating this complex landscape means understanding not just domestic regulations but also the intricate web of cybersecurity treaties U.S. is involved in. As we look towards 2026, the implications of these international agreements on individual data privacy and security are more profound than ever. This comprehensive guide aims to demystify the world of international cybersecurity law, providing practical solutions and insights for U.S. citizens to safeguard their personal data in an increasingly interconnected world.
The digital revolution has brought unprecedented convenience, but it has also opened doors to new and evolving threats. Cyberattacks, data breaches, and state-sponsored espionage are daily headlines, reminding us that our digital footprints are constantly at risk. While national laws like the California Consumer Privacy Act (CCPA) or sector-specific regulations like HIPAA offer some protection, the internet’s borderless nature means that data often travels across jurisdictions, falling under the purview of multiple legal frameworks. This is where cybersecurity treaties U.S. plays a critical role, attempting to establish common ground and cooperation among nations to combat cybercrime and protect digital assets.
Understanding these international agreements is not merely an academic exercise; it is a vital component of personal data protection. For U.S. citizens, knowing how these treaties influence data handling by multinational corporations, foreign governments, and even domestic entities can empower them to make informed decisions about their digital lives. This guide will delve into the major international cybersecurity agreements, their impact on U.S. citizens, and actionable steps you can take to enhance your personal data security by 2026.
Anúncios
The Evolving Landscape of International Cybersecurity Treaties by 2026
The international community has been grappling with cybersecurity challenges for decades, leading to a patchwork of bilateral, regional, and multilateral agreements. By 2026, several key cybersecurity treaties U.S. citizens should be aware of will continue to shape the global digital environment. These treaties aim to foster cooperation, establish norms of behavior in cyberspace, and provide mechanisms for mutual assistance in investigations and prosecutions of cybercrimes.
The Budapest Convention on Cybercrime: A Cornerstone
The Council of Europe’s Convention on Cybercrime, commonly known as the Budapest Convention, remains the most comprehensive international treaty on cybercrime. Adopted in 2001, it provides a common criminal justice framework for cybercrime and electronic evidence. The U.S. ratified this convention in 2006, making it a crucial part of its international cybersecurity strategy. By 2026, the convention’s influence will have expanded further, with more countries acceding to it, creating a broader, albeit still incomplete, global standard for addressing cybercrime.
Anúncios
For U.S. citizens, the Budapest Convention means that certain cybercrimes committed against them or by them, even if originating from or targeting other signatory countries, can be investigated and prosecuted with international cooperation. It standardizes definitions of cyber offenses, such as illegal access, data interference, and computer-related fraud, making it easier for law enforcement agencies across borders to collaborate. This cooperation is vital when personal data is compromised by actors operating outside U.S. jurisdiction.
Bilateral and Regional Agreements: Strengthening Specific Partnerships
Beyond multilateral treaties, the U.S. has also entered into numerous bilateral agreements with key allies and strategic partners. These agreements often focus on intelligence sharing, joint cyber defense exercises, and mutual legal assistance in specific cyber incidents. For instance, agreements with countries like the UK, Canada, and Australia (often under the ‘Five Eyes’ intelligence-sharing alliance) facilitate rapid responses to cross-border cyber threats affecting personal data. By 2026, these bilateral relationships are expected to deepen, reflecting the increasing sophistication and frequency of cyberattacks.
Regional initiatives also play a significant role. While the U.S. is not part of the European Union’s comprehensive data protection framework (GDPR), it engages with EU member states on cybersecurity matters. Discussions around data flows and privacy shield agreements, though often contentious, highlight the ongoing effort to reconcile different approaches to data protection across regions. The outcomes of these discussions directly impact U.S. citizens whose data is processed by European entities or vice versa.
Emerging Norms and Future Treaties: The Road Ahead
The landscape of international cybersecurity is constantly evolving, with ongoing debates at the United Nations and other international forums about establishing new norms of responsible state behavior in cyberspace. Discussions around preventing cyber warfare, protecting critical infrastructure, and upholding human rights in the digital sphere are gaining traction. While a universally binding treaty on these broader issues may still be years away, the principles being debated will undoubtedly influence future cybersecurity treaties U.S. might endorse or help shape.
For U.S. citizens, these evolving norms mean that the legal and ethical boundaries of state and non-state actor behavior in cyberspace are continually being refined. This has direct implications for the security of personal data, as stronger international consensus on what constitutes acceptable behavior can lead to more robust protections against state-sponsored hacking and surveillance.
How Cybersecurity Treaties Impact U.S. Citizens’ Personal Data
The direct impact of cybersecurity treaties U.S. on individual citizens might not always be immediately apparent, but their influence is far-reaching. These agreements primarily operate at a governmental and institutional level, but their effects trickle down to how personal data is collected, stored, processed, and protected by various entities.
Cross-Border Data Flows and Legal Jurisdiction
One of the most significant impacts concerns cross-border data flows. In an interconnected world, personal data of U.S. citizens can be stored on servers located in other countries, processed by foreign companies, or accessed by international law enforcement. Cybersecurity treaties provide frameworks for how governments request and share this data, aiming to balance national security interests with individual privacy rights. For example, mutual legal assistance treaties (MLATs), often influenced by the Budapest Convention, dictate the procedures for law enforcement agencies to request electronic evidence from other countries.
While these treaties facilitate investigations into cybercrime, they also raise concerns about surveillance and data access without adequate safeguards. U.S. citizens need to be aware that their data, when stored or processed abroad, may be subject to the laws of that foreign jurisdiction, which might offer different levels of privacy protection than U.S. law. The ongoing debates around data localization and data sovereignty underscore these complexities.
Enhanced Cybercrime Enforcement and Deterrence
By standardizing definitions of cybercrimes and establishing mechanisms for international cooperation, cybersecurity treaties enhance the ability of law enforcement agencies to track, apprehend, and prosecute cybercriminals. This increased enforcement capability acts as a deterrent, potentially reducing the overall incidence of cyberattacks that target personal data. When a U.S. citizen’s data is stolen by a hacker operating from another country, these treaties provide the legal pathways for the U.S. government to seek assistance in bringing the perpetrator to justice.
However, the effectiveness of this enforcement depends on the political will and technical capabilities of signatory nations. Loopholes, differing legal interpretations, and varying levels of commitment can hinder swift and effective action, leaving some U.S. citizens vulnerable despite the existence of treaties.
Influence on Corporate Data Handling Practices
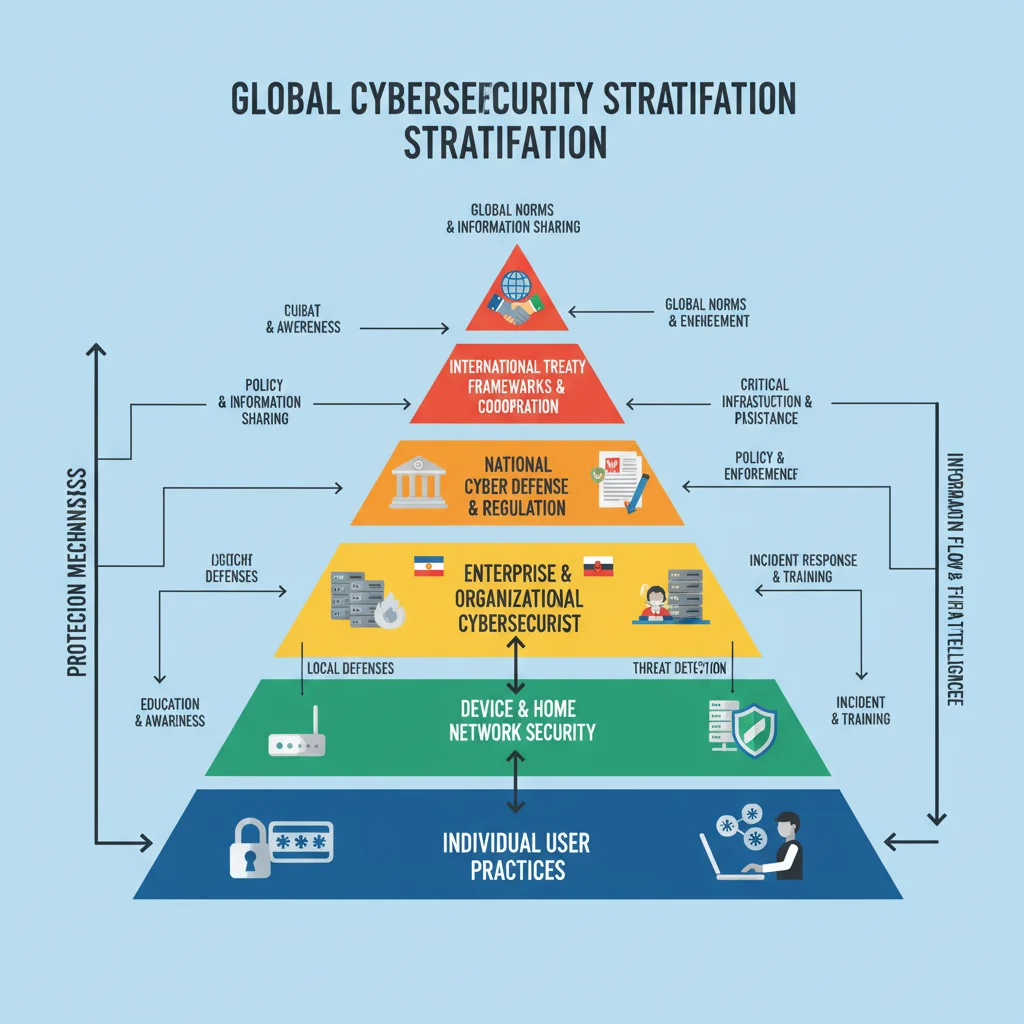
Multinational corporations operating across different jurisdictions are often caught between conflicting national and international data protection requirements. Cybersecurity treaties and related data protection agreements influence how these companies structure their global data handling policies. For instance, if a U.S. company processes data of EU citizens, it must adhere to GDPR, which often sets a higher bar for data protection than some U.S. laws. While GDPR is not a treaty, its principles and the EU’s influence on data protection standards can indirectly impact how U.S. companies handle all their user data, including that of U.S. citizens, to ensure compliance across their operations.
This means that global companies might adopt a ‘highest common denominator’ approach to data protection, elevating the security and privacy standards for all users. Conversely, a lack of strong international consensus on certain data protection aspects could lead to fragmented approaches, leaving gaps in protection for U.S. citizens whose data is handled by companies with less stringent standards in other parts of the world.
National Security and Critical Infrastructure Protection
Many cybersecurity treaties U.S. engages in also have a strong national security component, focusing on protecting critical infrastructure from cyberattacks. While seemingly distant from individual data, attacks on power grids, financial systems, or healthcare networks can have cascading effects that directly impact personal data. For example, a successful attack on a healthcare provider’s systems could expose millions of patient records. Treaties that promote information sharing on threats and vulnerabilities among nations contribute to a more secure global digital environment, indirectly benefiting individual data protection.
Practical Solutions for U.S. Citizens by 2026
Understanding the landscape of cybersecurity treaties U.S. is important, but what truly empowers U.S. citizens is knowing how to translate this knowledge into actionable steps for personal data protection. By 2026, embracing a proactive and informed approach to digital security will be non-negotiable.
1. Strong Password Hygiene and Multi-Factor Authentication (MFA)
This remains the foundational pillar of digital security. Use unique, complex passwords for every online account and enable MFA wherever possible. MFA adds an extra layer of security, making it significantly harder for unauthorized individuals to access your accounts even if they somehow obtain your password. By 2026, MFA should be a default for most critical online services, but it’s your responsibility to activate it.
2. Understand Data Privacy Policies and Terms of Service
While often lengthy and complex, taking the time to review the privacy policies and terms of service of the online services you use can reveal how your data is collected, used, and shared. Pay attention to sections that discuss data transfers across borders or sharing with third parties. If a policy seems vague or overly permissive, consider alternatives that prioritize user privacy. This is especially true for services that operate internationally, as they may be subject to different legal regimes than U.S. companies.
3. Utilize Privacy-Enhancing Technologies (PETs)
By 2026, PETs will be more accessible and user-friendly. These include:
- Virtual Private Networks (VPNs): Encrypt your internet connection and mask your IP address, making it harder for third parties to track your online activities and protecting your data when using public Wi-Fi.
- Encrypted Messaging Apps: Use end-to-end encrypted communication platforms for sensitive conversations, ensuring only the sender and intended recipient can read the messages.
- Privacy-Focused Browsers and Search Engines: Opt for browsers and search engines that prioritize user privacy by blocking trackers and not logging your search history.
4. Be Vigilant Against Phishing and Social Engineering
Cybercriminals constantly evolve their tactics. Phishing emails, smishing (SMS phishing), and vishing (voice phishing) remain prevalent methods to trick individuals into revealing personal data. Learn to identify suspicious communications, never click on unknown links, and always verify the sender before providing any information. Treat unsolicited requests for personal data with extreme skepticism, especially if they claim to be from a reputable organization.
5. Regularly Review and Manage Your Digital Footprint
Periodically audit your online accounts. Delete old accounts you no longer use, review privacy settings on social media and other platforms, and limit the amount of personal information you share publicly. The less data that is freely available about you online, the less vulnerable you are to targeted attacks and data aggregation efforts by malicious actors.
6. Stay Informed About Data Breaches and Security Alerts
Subscribe to reputable cybersecurity news sources and alerts. Knowing about recent data breaches, especially those involving services you use, allows you to take immediate action, such as changing passwords and monitoring your financial accounts for suspicious activity. The interconnected nature of data means that a breach in one service can have ripple effects on others.
7. Understand Your Rights Under U.S. Data Protection Laws
While this guide focuses on international treaties, understanding your rights under U.S. laws like CCPA (and potential future federal privacy laws) is crucial. These laws provide mechanisms for you to request access to your data, demand its deletion, or opt out of its sale. Familiarize yourself with these rights and exercise them when necessary.
The Role of Government and Industry in Data Protection
While individual actions are critical, the responsibility for protecting personal data is a shared one. Governments and industries also have significant roles to play, influenced heavily by the framework of cybersecurity treaties U.S. and international norms.
Governmental Initiatives and Policy Development
The U.S. government, guided by its commitments under various treaties, continues to invest in cybersecurity infrastructure, threat intelligence sharing, and public awareness campaigns. By 2026, we can expect further development of national cybersecurity strategies that integrate international cooperation. This includes supporting initiatives like the National Institute of Standards and Technology (NIST) Cybersecurity Framework, which provides voluntary guidelines for organizations to manage cyber risk. The government also plays a crucial role in negotiating and enforcing international agreements that protect U.S. citizens’ data.
Industry Best Practices and Compliance
Companies, particularly those operating globally, are increasingly adopting robust cybersecurity frameworks and adhering to international best practices. Compliance with regulations like GDPR, even if not directly applicable to U.S. citizens’ data, often leads to improved data protection standards across the board. The pressure from consumers and regulators, coupled with the reputational and financial costs of data breaches, incentivizes companies to prioritize cybersecurity. By 2026, expect to see more companies integrating advanced security measures, conducting regular security audits, and offering transparent data handling practices, partly driven by the evolving international legal landscape.
Challenges and Future Outlook for Cybersecurity Treaties U.S.
Despite the progress in establishing international cybersecurity frameworks, significant challenges remain. The rapid pace of technological change, the emergence of new cyber threats, and the geopolitical complexities of the digital world continually test the efficacy of existing treaties and the ability of nations to cooperate.
Jurisdictional Conflicts and Enforcement Gaps
One of the persistent challenges is the issue of jurisdictional conflicts. When a cyberattack originates from one country, targets individuals in another, and routes through servers in a third, determining which country’s laws apply and which jurisdiction has the authority to prosecute can be incredibly complex. While cybersecurity treaties U.S. attempts to streamline mutual legal assistance, the process can still be slow and cumbersome, especially when dealing with non-cooperative states or those with vastly different legal systems.
Balancing Security and Privacy
The ongoing tension between national security interests and individual privacy rights is another critical challenge. Governments often seek broad access to data for intelligence and law enforcement purposes, citing national security concerns. However, this can clash with citizens’ expectations of privacy and data protection. Future cybersecurity treaties U.S. will need to carefully navigate this balance, ensuring that mechanisms for international cooperation do not inadvertently lead to mass surveillance or erosion of fundamental rights.
The Rise of AI and Quantum Computing
The advent of advanced technologies like artificial intelligence (AI) and quantum computing presents both opportunities and threats to cybersecurity. AI can be used to enhance defensive measures, but it can also power more sophisticated attacks. Quantum computing, while still nascent, has the potential to break current encryption standards, necessitating entirely new approaches to data security. Future cybersecurity treaties will need to consider how to address these technological shifts, potentially by establishing norms for the responsible development and use of these technologies.
Lack of Universal Consensus
Despite efforts, a truly universal consensus on cybersecurity norms and legal frameworks remains elusive. Major global players often have divergent views on issues like cyber sovereignty, the role of state actors in cyberspace, and the definition of cyber warfare. This fragmentation can limit the reach and effectiveness of international treaties, creating safe havens for cybercriminals and state-sponsored actors. By 2026, while incremental progress is expected, a fully unified global approach to cybersecurity is unlikely.
Conclusion: Empowering U.S. Citizens in a Connected World
The digital world of 2026 will be more interconnected, more dynamic, and potentially more perilous than ever before. For U.S. citizens, protecting personal data requires a multi-faceted approach that combines individual vigilance with an understanding of the broader international legal and geopolitical landscape. The network of cybersecurity treaties U.S. participates in forms a critical, albeit imperfect, shield against global cyber threats, influencing everything from cross-border data flows to the prosecution of cybercriminals.
By staying informed about these treaties, understanding their implications, and adopting robust personal cybersecurity practices, U.S. citizens can empower themselves to navigate the complexities of the digital age. The responsibility for data protection is shared, but the ultimate power to safeguard one’s digital life lies in informed choices and proactive measures. As we move closer to 2026, let this guide serve as a blueprint for enhancing your personal data security and contributing to a more secure and trusted digital future.
