U.S. National Security 2026: Top 3 State-Sponsored Cyber Threats
Anúncios
U.S. National Security in 2026: Analyzing the Top 3 State-Sponsored Cyber Threats
The digital frontier has become the new battleground, and as we look towards 2026, the landscape of U.S. national security is increasingly defined by the sophisticated and relentless nature of state-sponsored cyber threats. These are not merely acts of espionage or data theft; they are strategic maneuvers aimed at undermining critical infrastructure, influencing democratic processes, and gaining a geopolitical advantage. Understanding these evolving threats is paramount for developing robust defense mechanisms and formulating proactive policies. This comprehensive analysis delves into the top three state-sponsored cyber threats projected to challenge US cyber threats 2026, examining their methodologies, potential targets, and the broader implications for global stability.
The pace of technological advancement means that cyber adversaries are constantly refining their tactics. What was considered cutting-edge cyber warfare five years ago might be commonplace today. State-sponsored groups, backed by significant financial and human resources, are at the forefront of this evolution, developing zero-day exploits, leveraging artificial intelligence for enhanced attack capabilities, and blurring the lines between cyber espionage and direct sabotage. The United States, with its vast digital footprint and interconnected critical systems, remains a prime target. The security of its government agencies, military networks, financial institutions, energy grids, and even public discourse is under constant scrutiny and assault. This article will shine a light on the most pressing concerns for US cyber threats 2026, offering insights into how these challenges might be met.
The Evolving Landscape of State-Sponsored Cyber Warfare
Before diving into the specifics of the top three threats, it’s crucial to grasp the overarching trends shaping state-sponsored cyber warfare. Firstly, the concept of ‘attribution’ remains a complex and often elusive challenge. Adversaries frequently employ sophisticated obfuscation techniques, proxy networks, and false flags to complicate efforts to definitively link an attack to a specific nation-state. This ambiguity allows for plausible deniability and escalates the difficulty of retaliatory measures, creating a grey zone in international law and conflict. Secondly, the integration of cyber operations with traditional intelligence gathering and military strategies is becoming seamless. Cyber attacks are no longer isolated incidents but often precursors or adjuncts to conventional geopolitical actions, serving to soften targets, sow discord, or collect vital intelligence.
Anúncios
Thirdly, the target scope has broadened significantly. While military and government networks remain high-value objectives, state-sponsored actors are increasingly targeting civilian critical infrastructure, academic institutions for research theft, and even private companies for industrial espionage or supply chain infiltration. This expansion reflects a strategy of ‘total information warfare,’ where every piece of data and every functional system can be leveraged for strategic advantage. Fourthly, the sophistication of attack vectors is on a steep upward curve. Beyond traditional phishing and malware, we are seeing the rise of supply chain attacks, where adversaries compromise trusted software or hardware vendors to inject malicious code into widely used products, impacting countless downstream users. The use of advanced persistent threats (APTs) that can reside undetected in networks for extended periods, continuously exfiltrating data or preparing for disruptive actions, is also a hallmark of these sophisticated groups.
Finally, the proliferation of offensive cyber capabilities among a growing number of nations means that the threat landscape is becoming more crowded and unpredictable. While a few major players have historically dominated this space, more countries are investing heavily in developing their own cyber warfare units, leading to a more complex and multi-polar digital threat environment. This makes addressing US cyber threats 2026 a multifaceted challenge that requires not only technological prowess but also astute diplomatic and intelligence efforts.
Threat 1: Advanced Persistent Threats (APTs) from Nation X (Hypothetical)
For the purposes of this analysis, let’s designate ‘Nation X’ as a highly advanced state actor with a proven track record of sophisticated cyber operations. Nation X’s primary objective in 2026 will likely continue to be the long-term infiltration and exfiltration of sensitive data from U.S. government agencies, defense contractors, and critical technology sectors. Their operations are characterized by an extreme level of stealth, patience, and adaptability. Unlike opportunistic hackers, APT groups from Nation X conduct extensive reconnaissance, often spending months or even years mapping target networks, identifying vulnerabilities, and crafting bespoke malware designed to evade detection by conventional security measures.
Anúncios
Their methodology typically involves a multi-stage approach. Initial access might be gained through highly targeted spear-phishing campaigns, exploiting zero-day vulnerabilities in widely used software, or compromising supply chains. Once inside a network, they establish persistent footholds, often creating multiple backdoors to ensure continued access even if one entry point is discovered and patched. They then move laterally through the network, escalating privileges and mapping internal systems to locate high-value targets. Data exfiltration is conducted discreetly, often in small, encrypted packets disguised as legitimate network traffic, making it incredibly difficult to detect without advanced behavioral analytics.
The targets of Nation X’s APTs are not arbitrary. They are carefully selected based on strategic national interests. In 2026, we can expect continued focus on intellectual property related to advanced defense technologies, aerospace, artificial intelligence, and biotechnology. Furthermore, intelligence gathering on U.S. foreign policy, economic strategies, and military readiness will remain a top priority. The long-term impact of such sustained espionage can be devastating, eroding America’s technological edge, compromising national security secrets, and providing adversaries with critical insights into U.S. capabilities and intentions. Countering these US cyber threats 2026 demands a shift from reactive defense to proactive threat hunting and intelligence-sharing across sectors.
The sophistication of Nation X’s APTs also extends to their ability to adapt and evolve. They often employ polymorphic malware, which changes its signature to avoid detection, and use encrypted communication channels that are challenging to intercept and analyze. Their command and control (C2) infrastructure is typically distributed globally, making it resilient to takedowns. Furthermore, these groups are known for their deep understanding of target organizations’ security postures, allowing them to exploit weaknesses in people, processes, and technology. This level of dedication and resource allocation signifies a persistent and dangerous adversary in the realm of US cyber threats 2026.
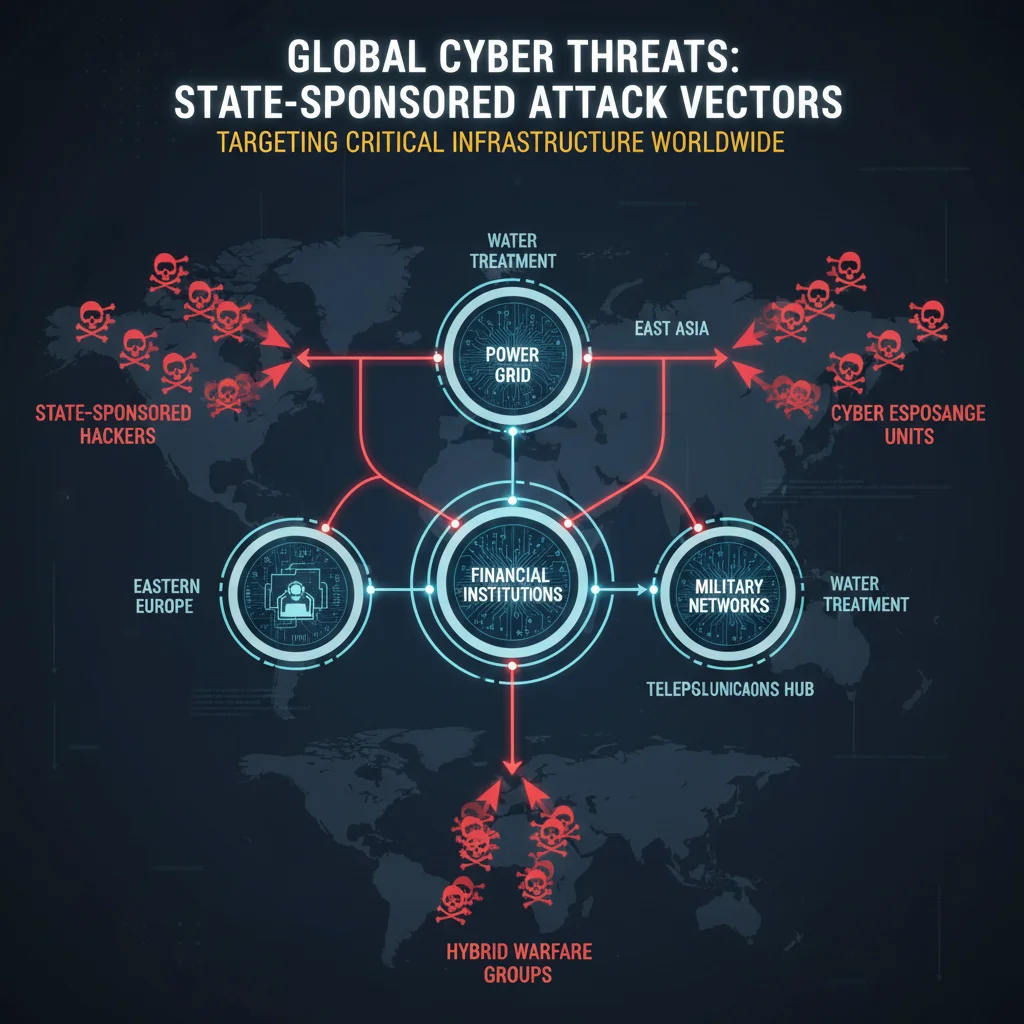
Threat 2: Disruptive and Destructive Attacks on Critical Infrastructure from Nation Y (Hypothetical)
Nation Y, our second hypothetical state actor, represents a power primarily focused on disruptive and potentially destructive cyber attacks against critical infrastructure. While espionage is often a component of their operations, their ultimate goal is to demonstrate capability, exert pressure, or even directly sabotage essential services. The targets include energy grids, water treatment facilities, transportation networks, and financial systems. The impact of such attacks can range from widespread service outages and economic disruption to direct threats to public safety and national morale.
The methodologies employed by Nation Y are often characterized by a willingness to cause immediate and noticeable impact. They may leverage custom-built malware designed to manipulate industrial control systems (ICS) and supervisory control and data acquisition (SCADA) systems, which are the digital brains behind much of our critical infrastructure. These systems, often legacy and less secure than traditional IT networks, present attractive targets. Attacks could involve denying access to operational controls, manipulating sensor readings to cause equipment malfunction, or even directly triggering physical damage to machinery.
Beyond direct manipulation, Nation Y might also engage in distributed denial-of-service (DDoS) attacks on critical network infrastructure, aiming to overwhelm systems and prevent legitimate access. Such attacks, while not directly destructive, can severely disrupt services and create chaos. The strategic implications of these attacks are profound. A successful attack on a major power grid, for example, could plunge vast regions into darkness, impacting everything from emergency services to financial transactions. A disruption to financial systems could trigger economic instability. These are not merely digital skirmishes; they are acts of economic and societal warfare.
The motivation behind Nation Y’s actions could be varied: to deter U.S. foreign policy actions, to retaliate against perceived aggressions, or to simply showcase their cyber prowess as a tool of statecraft. The challenge for US cyber threats 2026 in this context is not just preventing attacks but also building resilience into critical systems, ensuring rapid recovery capabilities, and establishing clear deterrence policies. This includes understanding the specific vulnerabilities of various infrastructure sectors and implementing tailored security measures. The interconnectedness of modern infrastructure means that a breach in one sector can have cascading effects across others, amplifying the potential for widespread disruption.
Threat 3: Information Warfare and Influence Operations from Nation Z (Hypothetical)
Our third state actor, Nation Z, specializes in information warfare and influence operations. While not directly destructive in the physical sense, these cyber threats aim to manipulate public opinion, sow discord, undermine democratic institutions, and erode trust in government and media. Their primary weapon is information – or rather, disinformation and propaganda – disseminated through sophisticated digital channels.
The tactics of Nation Z are highly adaptive and leverage the pervasive nature of social media platforms, online news outlets, and even seemingly innocuous online communities. They employ armies of trolls, bots, and fake accounts to amplify narratives, spread misinformation, and create artificial divisions within society. This can involve anything from fabricating news stories and doctoring images and videos (deepfakes) to exploiting existing societal tensions and polarizing political discourse. The goal is to create a fractured and distrustful populace, making it harder for the U.S. government to govern effectively and project a unified image on the global stage.
Beyond direct propaganda, Nation Z also engages in cyber operations designed to expose sensitive or embarrassing information (doxxing), often acquired through hacking, to further their influence objectives. This ‘hack-and-leak’ strategy can be used to discredit political figures, disrupt elections, or fuel public outrage. The cumulative effect of these operations can be a significant erosion of social cohesion and public trust, directly impacting national security by weakening the fabric of democracy itself. The challenge for US cyber threats 2026 in this domain is not just technological but also societal, requiring media literacy, critical thinking, and resilient democratic processes.
The sophistication of Nation Z’s campaigns lies in their ability to understand and exploit psychological vulnerabilities and cognitive biases. They use data analytics to identify target demographics and tailor their messages for maximum impact. They often operate in multiple languages and across various platforms, making their operations global in reach and difficult to contain. The blurred lines between legitimate online discourse and state-sponsored manipulation make it particularly challenging to combat. This threat demands a multi-faceted response, including technological solutions for identifying bots and misinformation, educational initiatives to bolster public resilience, and robust policy frameworks to address foreign interference without infringing on free speech.
Countering the Future of US Cyber Threats 2026: A Multi-Layered Approach
Addressing the complex and evolving landscape of US cyber threats 2026 requires a comprehensive, multi-layered, and collaborative approach. No single technology or policy can suffice against adversaries that are highly adaptable and well-resourced. The strategy must encompass technological advancements, policy reforms, international cooperation, and public engagement.
Technological Fortification and Innovation
- Zero Trust Architecture: Moving beyond traditional perimeter defenses, a zero-trust model assumes that no user or device, whether inside or outside the network, should be trusted by default. Every access request is verified, requiring continuous authentication and authorization. This significantly reduces the impact of successful initial breaches by limiting lateral movement.
- Advanced Threat Detection & Response: Investing in AI-driven behavioral analytics, machine learning for anomaly detection, and extended detection and response (XDR) solutions is crucial. These technologies can identify subtle indicators of compromise that human analysts or signature-based systems might miss, especially from APTs.
- Supply Chain Security: Given the prevalence of supply chain attacks, rigorous vetting of software and hardware vendors, implementing software bill of materials (SBOMs), and establishing secure development lifecycles are non-negotiable.
- Quantum-Resistant Cryptography: As quantum computing advances, current encryption standards may become vulnerable. Research and development into quantum-resistant cryptographic algorithms must be accelerated to protect long-term sensitive data.
- Resilience and Recovery: Beyond prevention, the ability to quickly detect, contain, and recover from a cyber attack is paramount. This includes robust backup strategies, incident response plans, and redundant systems for critical infrastructure.
Policy, Legislation, and Governance
- Clear Attribution and Deterrence Frameworks: The U.S. needs clearer policies for attributing state-sponsored attacks and a consistent framework for imposing consequences. This could involve economic sanctions, diplomatic pressure, or even proportional cyber retaliation, all aimed at raising the cost for adversaries.
- Public-Private Partnerships: Critical infrastructure is largely owned and operated by the private sector. Enhanced collaboration, intelligence sharing, and joint exercises between government agencies and private companies are essential for a unified defense.
- International Norms and Treaties: Advocating for and participating in international efforts to establish norms of responsible state behavior in cyberspace, and potentially cyber arms control treaties, can help de-escalate tensions and reduce the likelihood of destructive attacks.
- Cyber Workforce Development: A significant shortage of skilled cybersecurity professionals persists. Investing in education, training programs, and incentives to attract talent to both public and private sectors is vital.
Public Engagement and Education
- Media Literacy Initiatives: To counter information warfare, public education on critical media consumption, identifying misinformation, and understanding online manipulation tactics is crucial. This empowers citizens to be more resilient to influence operations.
- Cyber Hygiene Awareness: Basic cybersecurity practices, such as strong passwords, multi-factor authentication, and vigilance against phishing, remain the frontline defense for individuals and organizations alike. Public awareness campaigns can significantly reduce the attack surface.
The Economic and Geopolitical Impact of US Cyber Threats 2026
The ramifications of unmitigated US cyber threats 2026 extend far beyond technical breaches. Economically, successful state-sponsored cyber attacks can lead to staggering financial losses through intellectual property theft, business disruption, and the costs associated with recovery and remediation. The erosion of trust in digital systems can also stifle innovation and investment, impacting economic growth. Furthermore, the cost of maintaining and upgrading cybersecurity infrastructure represents a significant and growing expenditure for both government and industry, diverting resources that could otherwise be used for other developmental endeavors.
Geopolitically, the rise of state-sponsored cyber warfare complicates international relations. The ambiguity of attribution can lead to misunderstandings, miscalculations, and unintended escalation. A major cyber attack could be perceived as an act of war, potentially triggering conventional military responses. The ability of nations to project power in cyberspace also reshapes traditional alliances and rivalries, creating new dimensions of competition and cooperation. The U.S. must navigate this complex landscape with a clear understanding of its own capabilities, its adversaries’ intentions, and the potential for both conflict and collaboration in the digital realm.
Moreover, the continuous threat of cyber attacks can undermine public confidence in government institutions and democratic processes. If citizens lose faith in the integrity of elections or the security of their personal data held by government agencies, it can lead to political instability and social unrest. This makes the defense against US cyber threats 2026 not just a technical challenge, but a fundamental pillar of maintaining a stable and prosperous society.
Conclusion: A Resilient Future Amidst Persistent Threats
The year 2026 promises to be a period of intense cyber competition, with state-sponsored actors continuing to pose significant and evolving threats to U.S. national security. From the stealthy espionage of Nation X’s APTs, to the disruptive potential of Nation Y’s critical infrastructure attacks, and the insidious influence operations of Nation Z, the digital battleground demands constant vigilance and innovation. The U.S. cannot afford to be complacent; a proactive, adaptive, and collaborative defense strategy is essential.
By investing in cutting-edge cybersecurity technologies, fostering robust public-private partnerships, developing a skilled cyber workforce, and engaging in effective international diplomacy, the United States can build a more resilient digital future. The challenges posed by US cyber threats 2026 are formidable, but with a unified and strategic approach, the nation can safeguard its interests, protect its citizens, and maintain its leadership in an increasingly interconnected world.
The future of national security is inextricably linked to cybersecurity. Understanding, anticipating, and countering these state-sponsored threats will be the defining mission for policymakers, technologists, and citizens alike as we move deeper into the digital age. The commitment to a strong cyber defense is not just about protecting data; it’s about preserving sovereignty, economic stability, and democratic values in the face of persistent and sophisticated adversaries.
