Cybersecurity Threats 2026: Protecting US Critical Infrastructure
Anúncios
In the rapidly evolving digital landscape, the year 2026 looms as a critical juncture for US Critical Infrastructure Cybersecurity. The confluence of geopolitical tensions, advanced technological proliferation, and the increasing sophistication of adversarial nation-states has elevated the threat of state-sponsored cyberattacks to an unprecedented level. This comprehensive analysis aims to shed light on the projected cybersecurity threats, their potential impact on US national security, and the imperative for robust, proactive defense strategies.
The very fabric of modern society—from power grids and water treatment plants to financial systems and communication networks—relies on interconnected digital systems. These systems, collectively known as critical infrastructure, are not merely conveniences but the foundational pillars of national stability and economic prosperity. Any disruption, compromise, or destruction of these systems through cyber means could have catastrophic consequences, extending far beyond the digital realm into the physical world, impacting lives, livelihoods, and national sovereignty.
The United States, as a global leader in technology and a prominent geopolitical actor, remains a prime target for state-sponsored cyber espionage, sabotage, and disruption. Adversaries are not merely seeking to steal data or intellectual property; their objectives have broadened to include destabilizing societies, influencing political processes, and gaining strategic advantages in potential future conflicts. Understanding the nuances of these threats and developing resilient defenses is no longer an option but a national imperative.
The Evolving Threat Landscape: State-Sponsored Cyber Warfare in 2026
The year 2026 is anticipated to witness a significant escalation in the sophistication and audacity of state-sponsored cyberattacks. Unlike financially motivated cybercriminals, nation-state actors possess vast resources, highly skilled personnel, and a long-term strategic outlook, often operating with impunity under the guise of national interest. Their targets are meticulously chosen, and their methods are continually refined to bypass conventional defenses.
Anúncios
Advanced Persistent Threats (APTs) and Their Evolution
Advanced Persistent Threats (APTs) remain the cornerstone of state-sponsored cyber operations. These groups, often directly or indirectly affiliated with national governments, engage in prolonged, stealthy campaigns to infiltrate networks, establish footholds, and exfiltrate sensitive information or prepare for future disruptive actions. By 2026, APTs are expected to leverage even more advanced techniques, including:
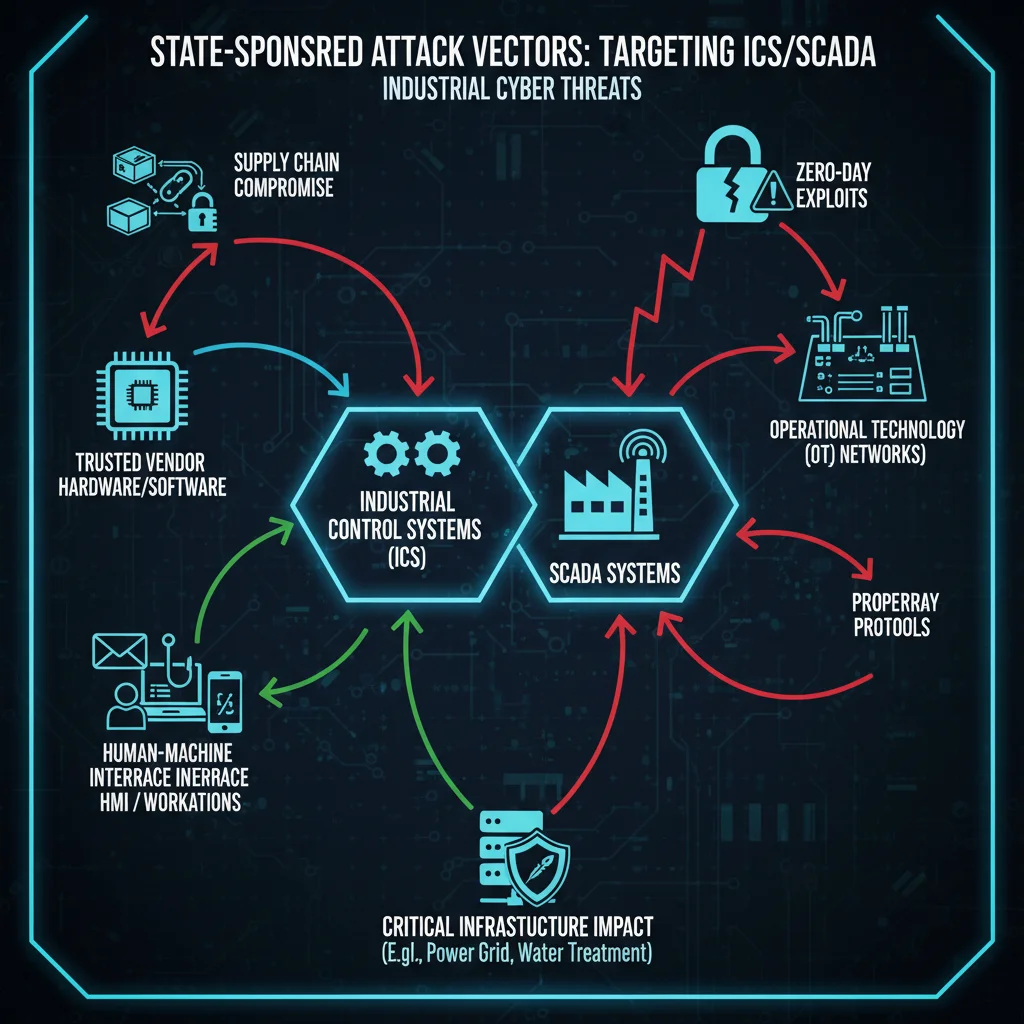
- Zero-Day Exploits: Increased reliance on previously unknown software vulnerabilities, making detection and prevention extremely challenging. The market for zero-day exploits is flourishing, and nation-states are among the most significant buyers.
- Supply Chain Attacks: Exploiting weaknesses in the software supply chain to inject malicious code into widely used products and services. This method offers a force multiplier, allowing attackers to compromise numerous targets simultaneously.
- AI and Machine Learning Integration: Adversaries will increasingly use AI and ML to automate reconnaissance, develop sophisticated malware variants that evade detection, and adapt attack strategies in real-time. This could lead to highly autonomous and evasive cyber weapons.
- Living Off the Land (LotL) Techniques: Minimizing the use of custom malware by leveraging legitimate tools and functionalities already present within target systems. This makes attacks harder to distinguish from legitimate network activity.
- Sophisticated Social Engineering: Beyond traditional phishing, state actors will employ highly personalized and contextually aware social engineering tactics, often incorporating deepfakes and AI-generated content to manipulate individuals within critical infrastructure organizations.
Targeting Critical Infrastructure: Specific Sectors at Risk
While all sectors are vulnerable, certain critical infrastructure domains are particularly attractive targets for state-sponsored adversaries due to their strategic importance and potential for widespread disruption:
- Energy Sector: Power grids, oil and gas pipelines, and nuclear facilities are prime targets for sabotage, aimed at causing widespread blackouts, industrial accidents, or economic paralysis. Disruptions here could have immediate and severe physical consequences.
- Water and Wastewater Systems: Compromising these systems could lead to contaminated water supplies, public health crises, and significant societal panic.
- Financial Services: Attacks aimed at disrupting banking systems, stock exchanges, or payment networks could trigger economic instability and erode public trust.
- Healthcare: Cyberattacks on hospitals and healthcare providers can disrupt patient care, compromise sensitive medical data, and even endanger lives, as seen with ransomware attacks.
- Transportation: Air traffic control, railway systems, and port operations are vulnerable to attacks that could cripple logistics, trade, and public movement.
- Communications: Disrupting internet service providers, cellular networks, or satellite communications can isolate communities, hinder emergency responses, and spread disinformation.
The Geopolitical Dimension: Who Are the Adversaries?
Identifying the specific state-sponsored actors is crucial for understanding their motivations, capabilities, and preferred tactics. While attribution is often challenging in the cyber domain, intelligence agencies continually monitor and assess the activities of several key players:
Anúncios
- Russia: Known for its highly capable and aggressive cyber units, historically targeting energy, government, and critical manufacturing sectors, often with a focus on disruption and influence operations.
- China: Primarily focused on intellectual property theft, economic espionage, and gaining strategic advantage through long-term infiltration of defense, technology, and critical infrastructure networks.
- Iran: Increasingly sophisticated, often targeting financial institutions, energy companies, and government entities, frequently in retaliation for perceived provocations.
- North Korea: Utilizes cyber operations, particularly ransomware and cryptocurrency theft, as a means of generating revenue to circumvent international sanctions, alongside strategic espionage.
These nation-states operate with varying degrees of deniability, often employing proxies or front organizations to mask their involvement. The blurred lines between state-sponsored, state-affiliated, and purely criminal groups further complicate the attribution landscape, making a unified defense strategy for US Critical Infrastructure Cybersecurity essential.
Impact on US National Security
The potential impact of successful state-sponsored cyberattacks on US national security extends across multiple dimensions:
Economic Disruption and Loss
A major cyberattack on critical infrastructure could lead to massive economic losses. Disruption of financial markets, energy supply, or transportation networks could halt commerce, cause widespread unemployment, and trigger a recession. The cost of recovery, both financial and in terms of lost productivity, would be immense.
Erosion of Public Trust and Social Instability
Public trust in government and essential services is a cornerstone of a stable society. A successful cyberattack that leads to prolonged outages of utilities, widespread data breaches, or manipulation of information could severely erode this trust, potentially leading to social unrest and political instability. The ability of adversaries to spread disinformation during or after an attack further amplifies this risk.
Physical Damage and Loss of Life
Perhaps the most severe consequence, cyberattacks on operational technology (OT) systems within critical infrastructure (e.g., industrial control systems, SCADA) can have direct physical consequences. Tampering with industrial processes could lead to equipment damage, environmental disasters, or even loss of life, turning a digital attack into a kinetic one.
Compromise of Sensitive Data and Intelligence
Beyond immediate disruption, state-sponsored actors consistently seek to exfiltrate sensitive government data, military intelligence, and proprietary technological secrets. Such compromises can undermine national defense capabilities, provide adversaries with strategic advantages, and impact long-term economic competitiveness.
Weakening of Military Readiness and Capabilities
The US military relies heavily on interconnected digital systems for everything from logistics and communications to weapon systems and intelligence gathering. Cyberattacks on defense industrial base (DIB) companies or military infrastructure could degrade readiness, compromise operational security, and hinder the ability to project power or respond to crises effectively.
Strategies for Enhancing US Critical Infrastructure Cybersecurity
Addressing the multifaceted challenges posed by state-sponsored cyber threats requires a comprehensive, multi-layered approach involving government agencies, private sector entities, and international partners. Proactive measures, rather than reactive responses, are paramount.
Strengthening Public-Private Partnerships
Critical infrastructure is largely owned and operated by the private sector, making robust collaboration between government and industry indispensable. This includes:
- Information Sharing: Establishing secure and timely mechanisms for sharing threat intelligence, vulnerabilities, and best practices between government agencies (e.g., CISA, NSA, FBI) and critical infrastructure operators.
- Joint Exercises: Conducting regular, realistic cyber exercises that simulate state-sponsored attacks to test response plans, identify gaps, and improve coordination across sectors.
- Incentivizing Cybersecurity Investments: Government initiatives, tax breaks, or regulatory frameworks that encourage private companies to invest in advanced cybersecurity measures and adopt resilient architectures.
Investing in Advanced Cybersecurity Technologies
Staying ahead of sophisticated adversaries requires continuous investment in cutting-edge technologies. Key areas include:
- AI and Machine Learning for Defense: Deploying AI-powered solutions for anomaly detection, threat hunting, and automated response to identify and neutralize threats more rapidly than human analysts alone.
- Zero Trust Architectures: Implementing a ‘never trust, always verify’ security model, where every user, device, and application is authenticated and authorized before accessing resources, regardless of its location.
- Quantum-Resistant Cryptography: Research and development into cryptographic algorithms that can withstand attacks from future quantum computers, protecting long-term data confidentiality.
- Operational Technology (OT) Security: Specializing in security solutions for industrial control systems (ICS) and SCADA environments, which have unique vulnerabilities compared to traditional IT networks. This includes network segmentation, immutable systems, and continuous monitoring.
Enhancing Cyber Workforce Development
The shortage of skilled cybersecurity professionals is a significant national security vulnerability. Addressing this requires:
- Education and Training Programs: Expanding university programs, vocational training, and certification initiatives to cultivate a larger and more diverse cybersecurity talent pool.
- Recruitment and Retention: Implementing competitive compensation, career development opportunities, and incentives to attract and retain top talent in both government and critical infrastructure sectors.
- Cyber Ranges and Simulations: Providing hands-on training environments where professionals can develop and hone their skills in realistic attack and defense scenarios.
Proactive Threat Hunting and Offensive Capabilities
A purely defensive posture is insufficient. The US must maintain and enhance its capabilities for:
- Threat Intelligence: Continuously gathering and analyzing intelligence on adversarial capabilities, intentions, and attack methodologies to anticipate threats.
- Proactive Threat Hunting: Actively searching for undetected threats within networks, rather than waiting for alerts.
- Deterrence and Retaliation: Developing and clearly communicating a robust cyber deterrence strategy, coupled with the capability to impose costs on adversaries who engage in malicious cyber activities against US interests.
International Cooperation and Norms
Cybersecurity is a global challenge that transcends national borders. International cooperation is essential for:
- Establishing Cyber Norms: Working with allies and international bodies to develop and enforce global norms of responsible state behavior in cyberspace, holding malicious actors accountable.
- Mutual Assistance Treaties: Developing agreements for mutual assistance in responding to and recovering from major cyberattacks.
- Capacity Building: Assisting allied nations in strengthening their own cyber defenses, particularly those with critical infrastructure interconnected with US systems.
The Role of Government Agencies in Safeguarding US Critical Infrastructure Cybersecurity
Several key government agencies play pivotal roles in the multifaceted effort to protect US Critical Infrastructure Cybersecurity:
Cybersecurity and Infrastructure Security Agency (CISA)
CISA is at the forefront of the civilian cyber defense effort. Its mission is to lead the national effort to understand, manage, and reduce risk to the cyber and physical infrastructure. CISA works directly with critical infrastructure owners and operators to provide threat intelligence, vulnerability assessments, and incident response support. Their role in facilitating information sharing between the government and the private sector is invaluable.
National Security Agency (NSA)
The NSA is responsible for signals intelligence (SIGINT) and ensuring the security of US national security systems. Its expertise in offensive and defensive cyber operations provides critical insights into adversary capabilities and helps inform national cybersecurity strategies. The NSA often works in conjunction with other agencies to provide highly specialized technical assistance.
Federal Bureau of Investigation (FBI)
The FBI leads investigations into cyber-crimes and state-sponsored cyber intrusions. By attributing attacks and prosecuting cybercriminals and state actors when possible, the FBI plays a crucial role in deterring future attacks and bringing justice to victims. Their close coordination with intelligence agencies provides a holistic view of the threat landscape.
Department of Energy (DOE)
Given the critical importance of the energy sector, the DOE plays a significant role in securing energy infrastructure against cyber threats. This includes research into resilient energy systems, developing best practices for operational technology security, and collaborating with energy companies to enhance their defensive postures.
Department of Defense (DoD) and US Cyber Command (USCYBERCOM)
The DoD and US Cyber Command are responsible for defending military networks and conducting offensive cyber operations when directed. While their primary focus is military systems, their capabilities and intelligence are vital for understanding the broader state-sponsored threat landscape and contributing to national cyber defense efforts.
Legislation and Policy Frameworks
Effective cybersecurity requires a robust legal and policy framework to guide actions and define responsibilities. Key legislative and policy initiatives include:
- Executive Orders: Presidential Executive Orders have frequently been used to direct federal agencies to improve cybersecurity, enhance information sharing, and develop frameworks for critical infrastructure protection.
- NIST Cybersecurity Framework: The National Institute of Standards and Technology (NIST) Cybersecurity Framework provides a voluntary, risk-based approach for organizations to manage and reduce cybersecurity risk. It is widely adopted across various sectors.
- Sector-Specific Regulations: Many critical infrastructure sectors (e.g., energy, finance, healthcare) have specific regulatory requirements (e.g., NERC CIP for the electricity sector, HIPAA for healthcare) that mandate certain cybersecurity standards.
- Cyber Incident Reporting Legislation: Recent legislation aims to improve transparency and information sharing by mandating critical infrastructure entities and federal agencies to report significant cyber incidents to CISA.
These frameworks are constantly evolving to keep pace with the dynamic threat landscape, aiming to create a more secure and resilient digital environment for US Critical Infrastructure Cybersecurity.
Conclusion: A Call for Unified Cyber Resilience
The cybersecurity threats facing US critical infrastructure in 2026 are complex, persistent, and carry profound implications for national security. State-sponsored actors, armed with advanced tools and strategic objectives, pose an existential challenge that demands an equally sophisticated and unified response. Protecting US Critical Infrastructure Cybersecurity is not merely a technical problem; it is a national security imperative that requires constant vigilance, innovative solutions, and unwavering collaboration across all levels of government and industry.
By prioritizing public-private partnerships, investing in cutting-edge technologies, fostering a skilled cyber workforce, and engaging in proactive defense and international cooperation, the United States can build a more resilient and secure digital future. The stakes are too high to do otherwise. The continuous evolution of threats necessitates a dynamic and adaptable defense strategy, ensuring that the foundational pillars of US society remain impervious to the designs of its adversaries.
